MC●MARK COOK / CURRICULUM VITAE
SECURITY. GOVERNANCE. CLARITY.
LOCK & KEY / 001
SECURITY BY DESIGN

MARK
COOK

Senior Information
Security Analyst

Turning technical complexity
into confident security decisions.

↓
SWINDON, UNITED KINGDOMSCROLL TO EXPLORE ↓

Security with
perspective.

I connect governance with the realities of security operations. Building stronger controls, clearer decisions and a more resilient organisation.

Senior Information Security Analyst leading governance, assurance and security improvement programmes across cloud, identity and operations. Combines ISO 27001-aligned ISMS design with hands-on incident response and technical assurance. At OPEN Health, contributed to a 134-point CyberVadis improvement, from 801 to 935. Trusted to turn technical findings into clear risk decisions, coordinate delivery across teams and suppliers, and brief senior stakeholders.

Download my CV ↗
ASSURANCE
801↗935

Stronger CyberVadis performance

Contributed to a 134-point increase through policy development, assurance evidence and cross-functional governance.

GOVERNANCE
ISO 27001

A framework built for practice

Designed an aligned ISMS spanning policies, control frameworks, risk management and governance structures.

TECHNICAL ASSURANCE
Cloud & beyond

Assurance from scope to remediation

Led penetration-testing programmes across AWS, Azure, infrastructure and business applications.

Where strategy
meets execution.

2018 — PRESENT
OPEN Health /

Senior Information Security Analyst

Promoted to Senior · London, UK
October 2022 — Present

01 Leadership, governance & delivery +
  • Contributed to raising CyberVadis from 801 to 935 by coordinating assurance evidence, policy development and cross-functional governance.
  • Designed an ISO 27001-aligned ISMS covering control frameworks, risk-management processes and governance; progressed policies through review and approval.
  • Led supplier security assurance, translating assessment findings into risks and coordinating remediation with suppliers and accountable internal owners.
  • Led penetration-testing programmes across AWS, Azure, infrastructure and business applications, managing scope, external testers and remediation.
  • Assessed cloud architectures and low-level designs for identity, access, logging and infrastructure control gaps; advised stakeholders on risk and remediation.
  • Coordinated live incident investigation, containment and recovery; authored incident-response and ransomware playbooks for consistent escalation and action.
  • Designed Sentinel enrichment and automation strategies; strengthened Entra ID, MFA, PIM and Conditional Access and coordinated AWS federation and SSO.
  • Led Mimecast, DMARC and KnowBe4 initiatives; delivered executive briefings connecting incidents, vulnerabilities and controls to business risk.
Neptune Europe Ltd /

Information Security Engineer

August 2020 — October 2022

01 Security strategy & engineering +
  • Led regional information security operations, translating global security strategy into transformation plans and practical control improvements.
  • Delivered board-level reporting on reputational risk, cost and delivery timelines to support executive prioritisation and alignment.
  • Integrated threat intelligence and compliance requirements into risk management across hybrid environments.
  • Authored and governed the IT Security Policy; maintained policies, procedures and registers to support consistent controls and audit readiness.
  • Implemented information protection and governance frameworks supporting GDPR compliance and delivered Cyber Essentials certification.
  • Implemented and operated SIEM and IDS capabilities; configured Defender ATP and Cloud App Security for endpoint and cloud threat monitoring.
  • Deployed Conditional Access, MFA and PIM; enforced least privilege and governed IAM and SharePoint security for controlled access and collaboration.
  • Led vulnerability remediation and testing of fixes; developed and enforced endpoint DLP policies to protect sensitive information.
Neptune Europe Ltd /

Infrastructure Engineer

February 2018 — August 2020

01 Infrastructure & security foundations +
  • Segmented business networks and established the company’s first IT Security Policy, embedding security into infrastructure operations.
  • Managed Dell Compellent storage, Hyper-V and virtual-machine environments alongside Azure infrastructure and Azure DevOps.
  • Managed Intune, Autopilot, Azure Arc and Azure Update Manager to support endpoint provisioning and cloud infrastructure administration.
  • Administered enterprise applications, identity-provider SSO and Conditional Access, including access arrangements for legacy applications.
  • Worked across Microsoft Security and Purview capabilities for IoT security, vulnerability management, threat intelligence, labelling and classification.
  • Applied Defender for Endpoint, Defender for Identity, Key Vault, CIEM and Identity Protection capabilities across infrastructure and identity workflows.

A connected
security skill set.

01 / GOVERN

Governance & assurance

ISO/IEC 27001 · ISMS development · Risk management · Audit readiness · Third-party risk · Policy authoring · Programme delivery

02 / PROTECT

Cloud & identity

Azure · AWS · Entra ID · Conditional Access · PIM · MFA · SSO & federation · Microsoft 365 · Intune · Azure Arc

03 / RESPOND

Operations & investigation

Defender XDR · Microsoft Sentinel · Incident response · Ransomware playbooks · Vulnerability management · Penetration-test management

04 / ENABLE

Tools & communication

PowerShell · KQL · Azure CLI · Microsoft Graph · Mimecast · DMARC · KnowBe4 · SecurityScorecard · CyberVadis · Executive reporting

The full
professional picture.

Explore my experience, expertise and achievements in a dedicated CV view. Download the same two-page layout as a PDF.
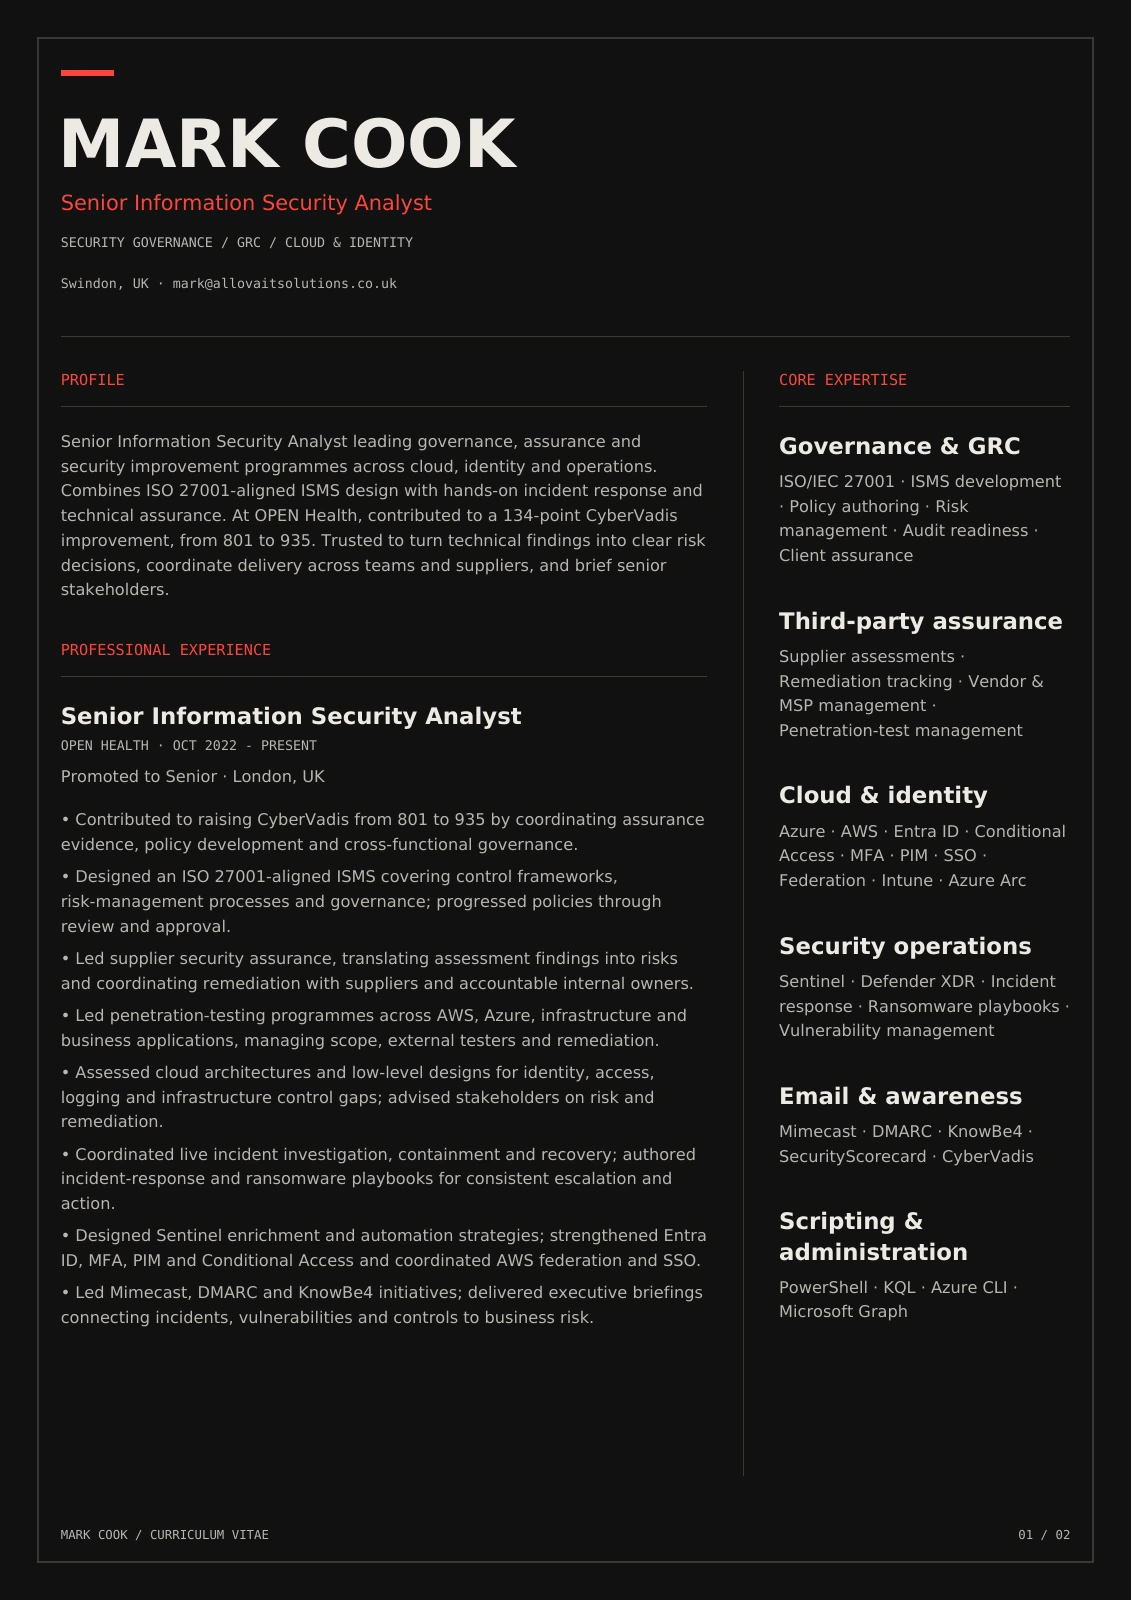
Preview of Mark Cook’s formatted CV
THE NEXT CHAPTER

Let’s talk
security.↗

Exploring opportunities in
Information Security Management,
GRC & Security Governance.

mark@allovaitsolutions.co.uk ↗Download CV ↗